Brief
Project overview
Designed and deployed a security operations dashboard pattern now running at two scales: in production across a multi-site enterprise network (a multi-site apparel manufacturer with domestic and international operations) and continuously on a self-hosted homelab that doubles as a testbed for new monitoring and AI-ops techniques before they go anywhere near production.
The enterprise deployment covers real operational stakes: network exposure across manufacturing and office sites, service uptime for ERP-adjacent systems, and the kind of continuous monitoring that turns 'we think we're secure' into 'we can prove it, right now.'
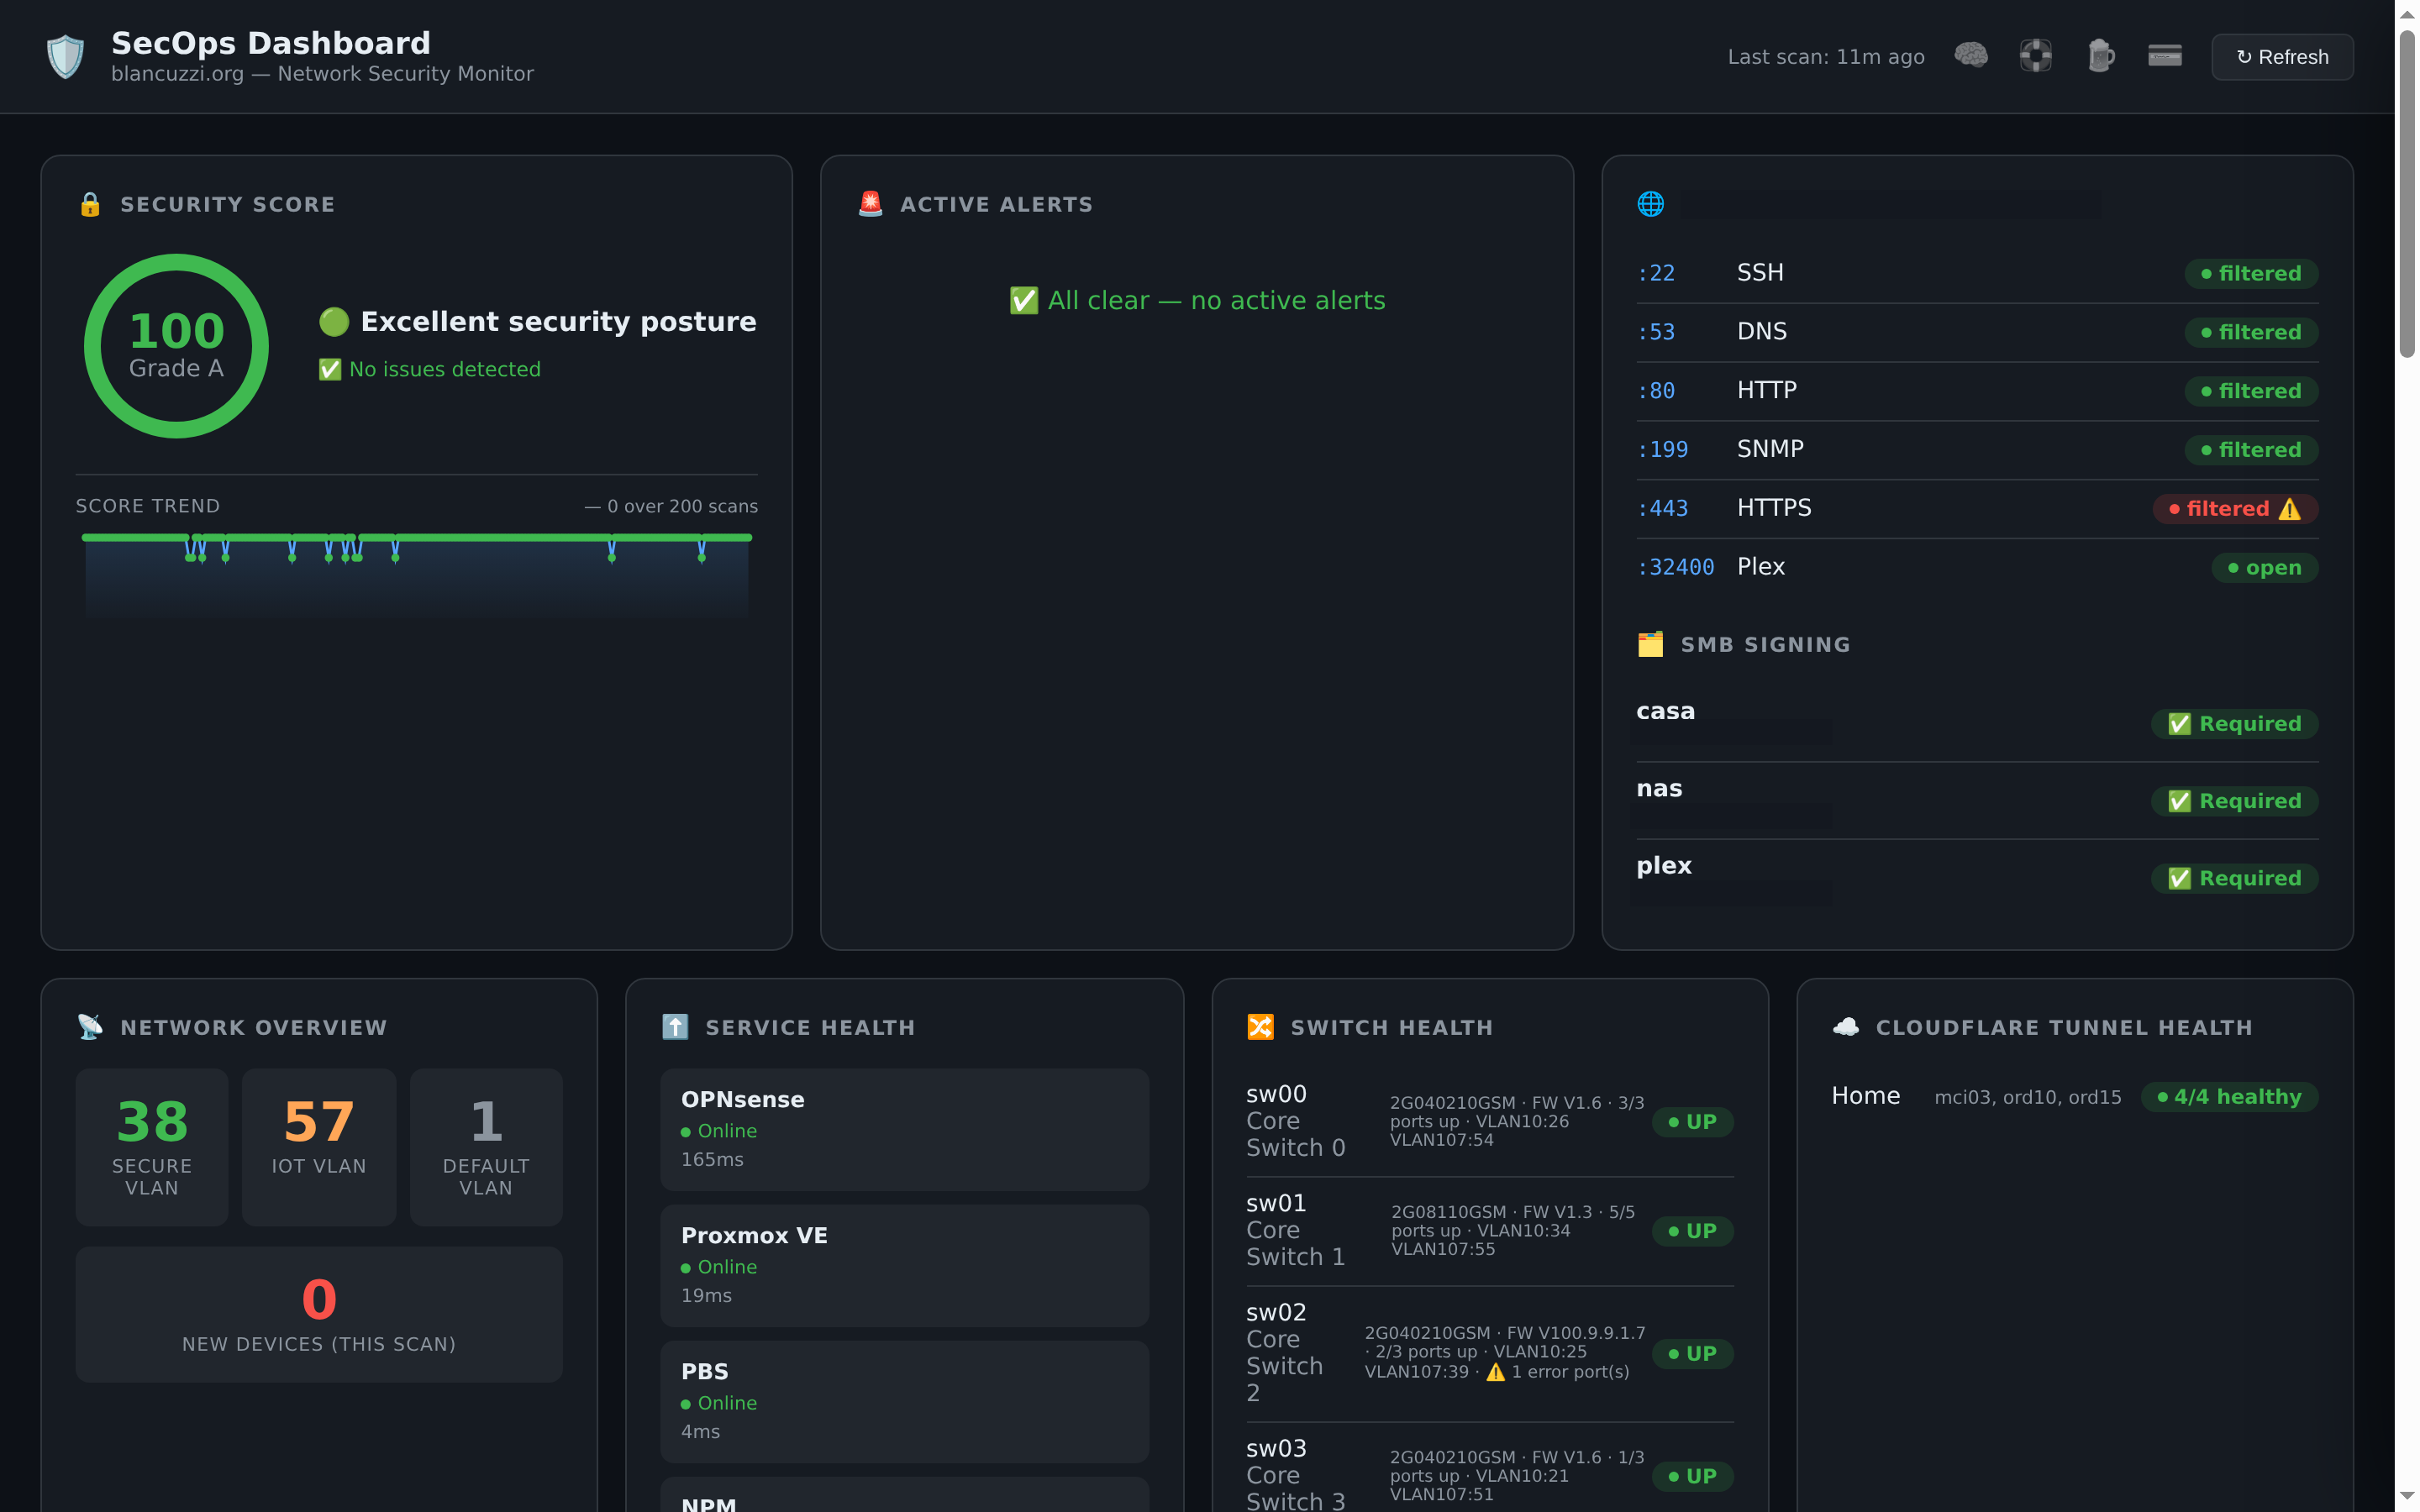
Capabilities demonstrated in the pictured instance (homelab, sanitized for publication):
- Continuous WAN exposure and port-filtering checks against the perimeter firewall
- SMB signing and internal host hardening checks
- Service health monitoring across public-facing endpoints with SSL cert expiry alerts
- Domain expiry tracking to prevent surprise lapses
- Multi-provider AI routing dashboard: local (Ollama) and cloud (Copilot, OpenAI, DeepSeek) providers, live cost/credit burn-rate tracking, per-provider session usage
- Automated alerting (15-min interval) and scheduled digest reporting
- Cron job health/routing visibility for scheduled automation tasks
The point isn't the homelab. It's that the same discipline — know your exposure, monitor continuously, automate the noise, keep a human reviewing the signal — scales down to a personal lab and up to a multi-site manufacturing network without changing the underlying approach. This instance is also where AI agent cost/performance tradeoffs across providers get evaluated before recommending them to clients.