Bringing Identity Governance Out of the Dark: Active Directory and IBM i Account Auditing at Scale
The Challenge
A 20+ year old identity estate — Active Directory plus a parallel IBM i user profile store — had never been audited end to end. Accounts accumulate for decades of manufacturing operations, M&A, and staff turnover with no attrition process: nobody was disabling what nobody was using. The actual scale of the problem was unknown because nobody had measured it. Guesses about 'stale accounts' or 'who has admin rights' were opinions, not numbers.
Our Solution
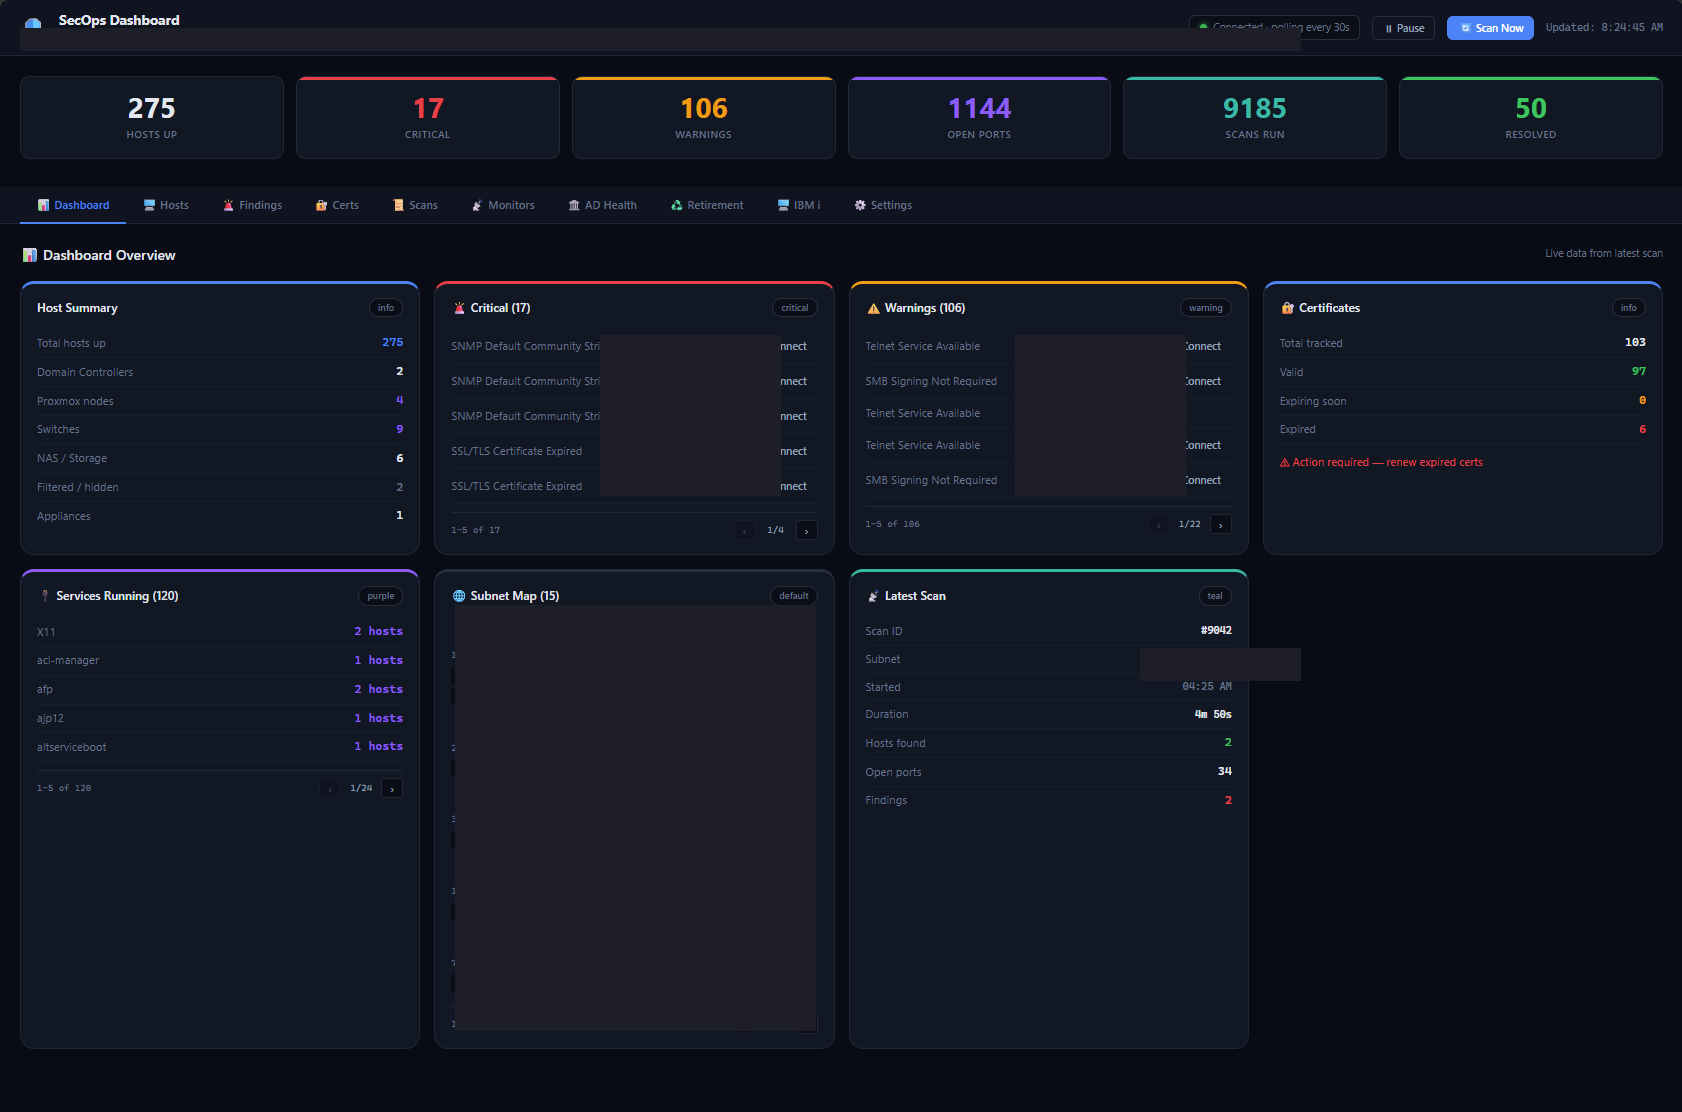
Built a read-only identity posture audit against the live directory using a dedicated, least-privilege service account and paged LDAP queries (a naive single-page query silently truncates around 1,000 entries and under-reports a directory this size — worth knowing before trusting any AD report tool). The audit measures privileged group membership, password policy weaknesses, account staleness by last logon, and computer object sprawl versus actually-live hosts, cross-checked against network scan data so 'enabled' and 'real' are two different questions with two different answers.
The same discipline was applied to the IBM i side, auditing user profiles for dormant accounts, excess authority, and default-password exposure directly against QSYS2 system views rather than relying on decades-old assumptions about who has access.
Remediation is intentionally staged and human-gated: findings are surfaced with severity and evidence, then acted on in phases, site-by-site, starting with a pilot, disabling rather than deleting, and keeping a full restore path for every account touched. Nothing is auto-remediated — the tooling's job is to make the decision visible, not to make the decision.
Results & Impact
• Directory-wide measurement replaced guesswork: privileged group membership, password policy gaps, and stale account counts are now known numbers, not impressions
• Computer object sprawl found running roughly 3-4x the actual live host count — a real attack surface that had no owner and no cleanup cadence
• A large share of enabled service and privileged accounts identified as unnecessary domain-level privilege — remediated via delegation instead of blanket admin rights
• Staged, disable-not-delete remediation process shipped with a pilot phase and full reversibility, so cleanup doesn't become its own outage risk
• Same audit-before-you-touch-it approach extended to the IBM i user profile store, closing the gap between two identity systems that had never been reconciled against each other
Project Details
Multi-site apparel manufacturer
Apparel Manufacturing
Ongoing, initial audit and tooling build 3 weeks
Related Case Studies
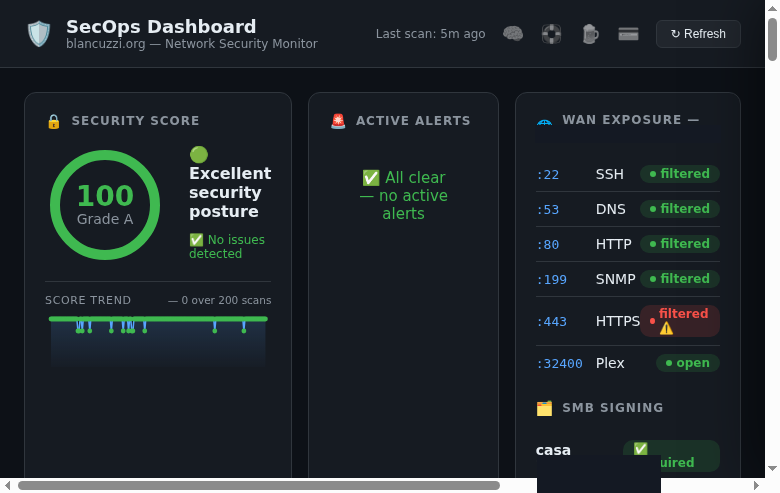
Continuous Security Monitoring Across a Multi-Site Manufacturing Network